I’d like to use FN APIs to integrate with Splunk and SIEM / Security systems. Has anyone else done this?
Solved
Splunk / SIEM Integration

Best answer by GTurner
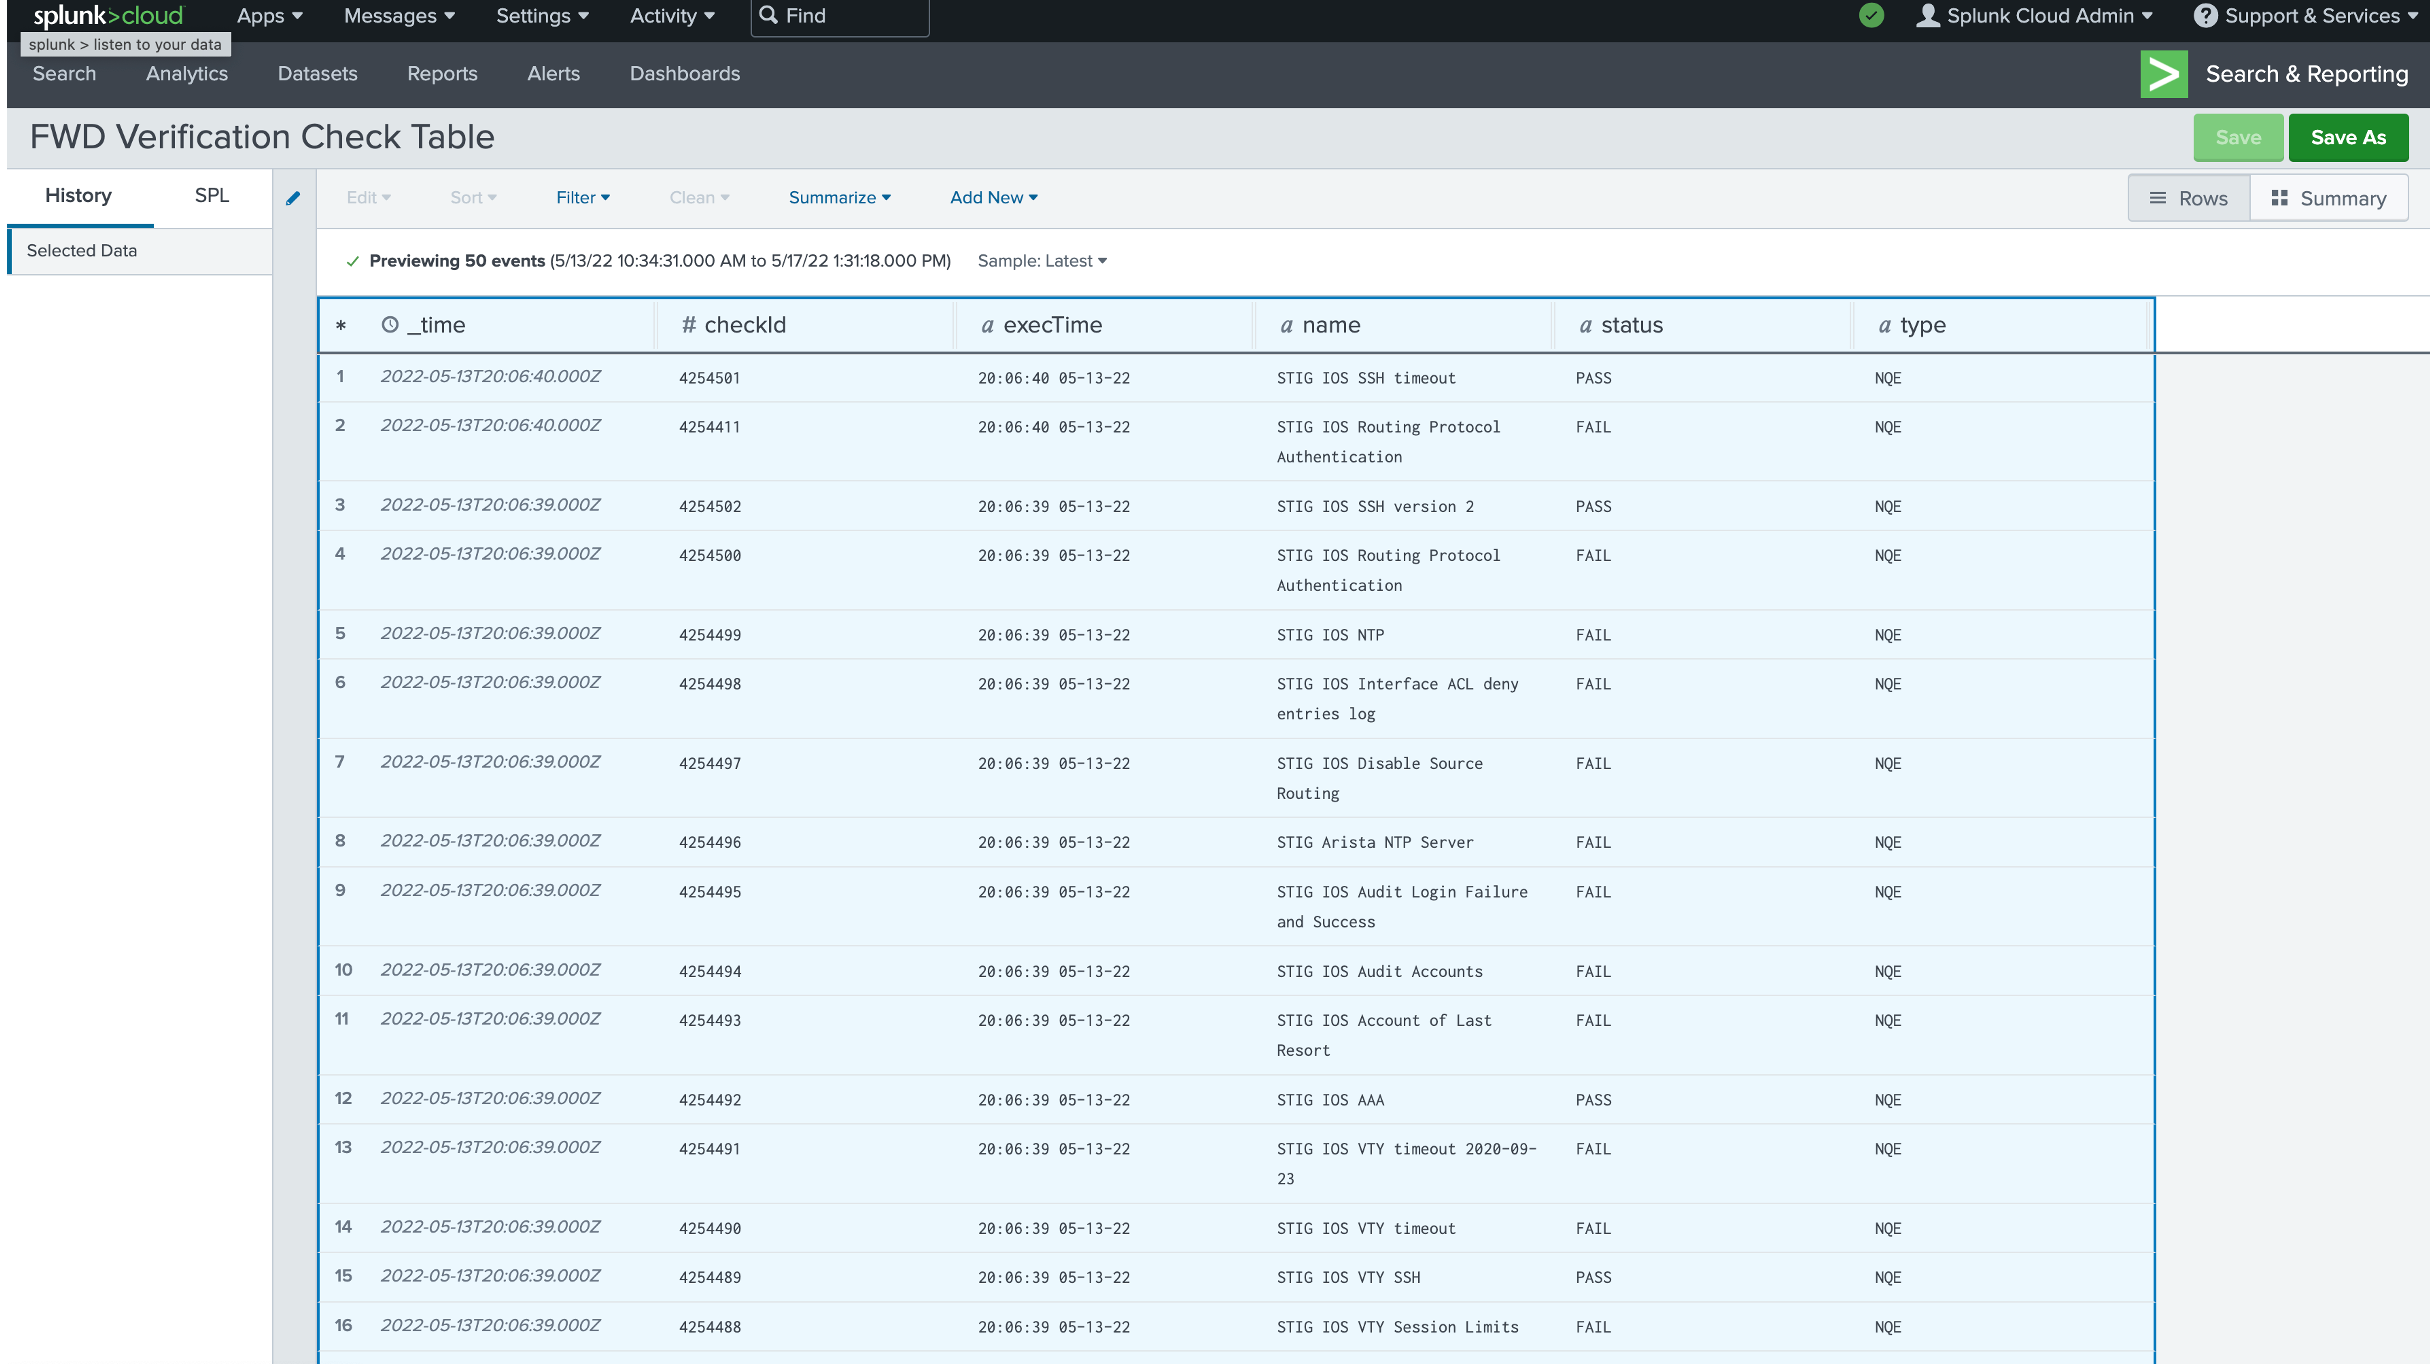
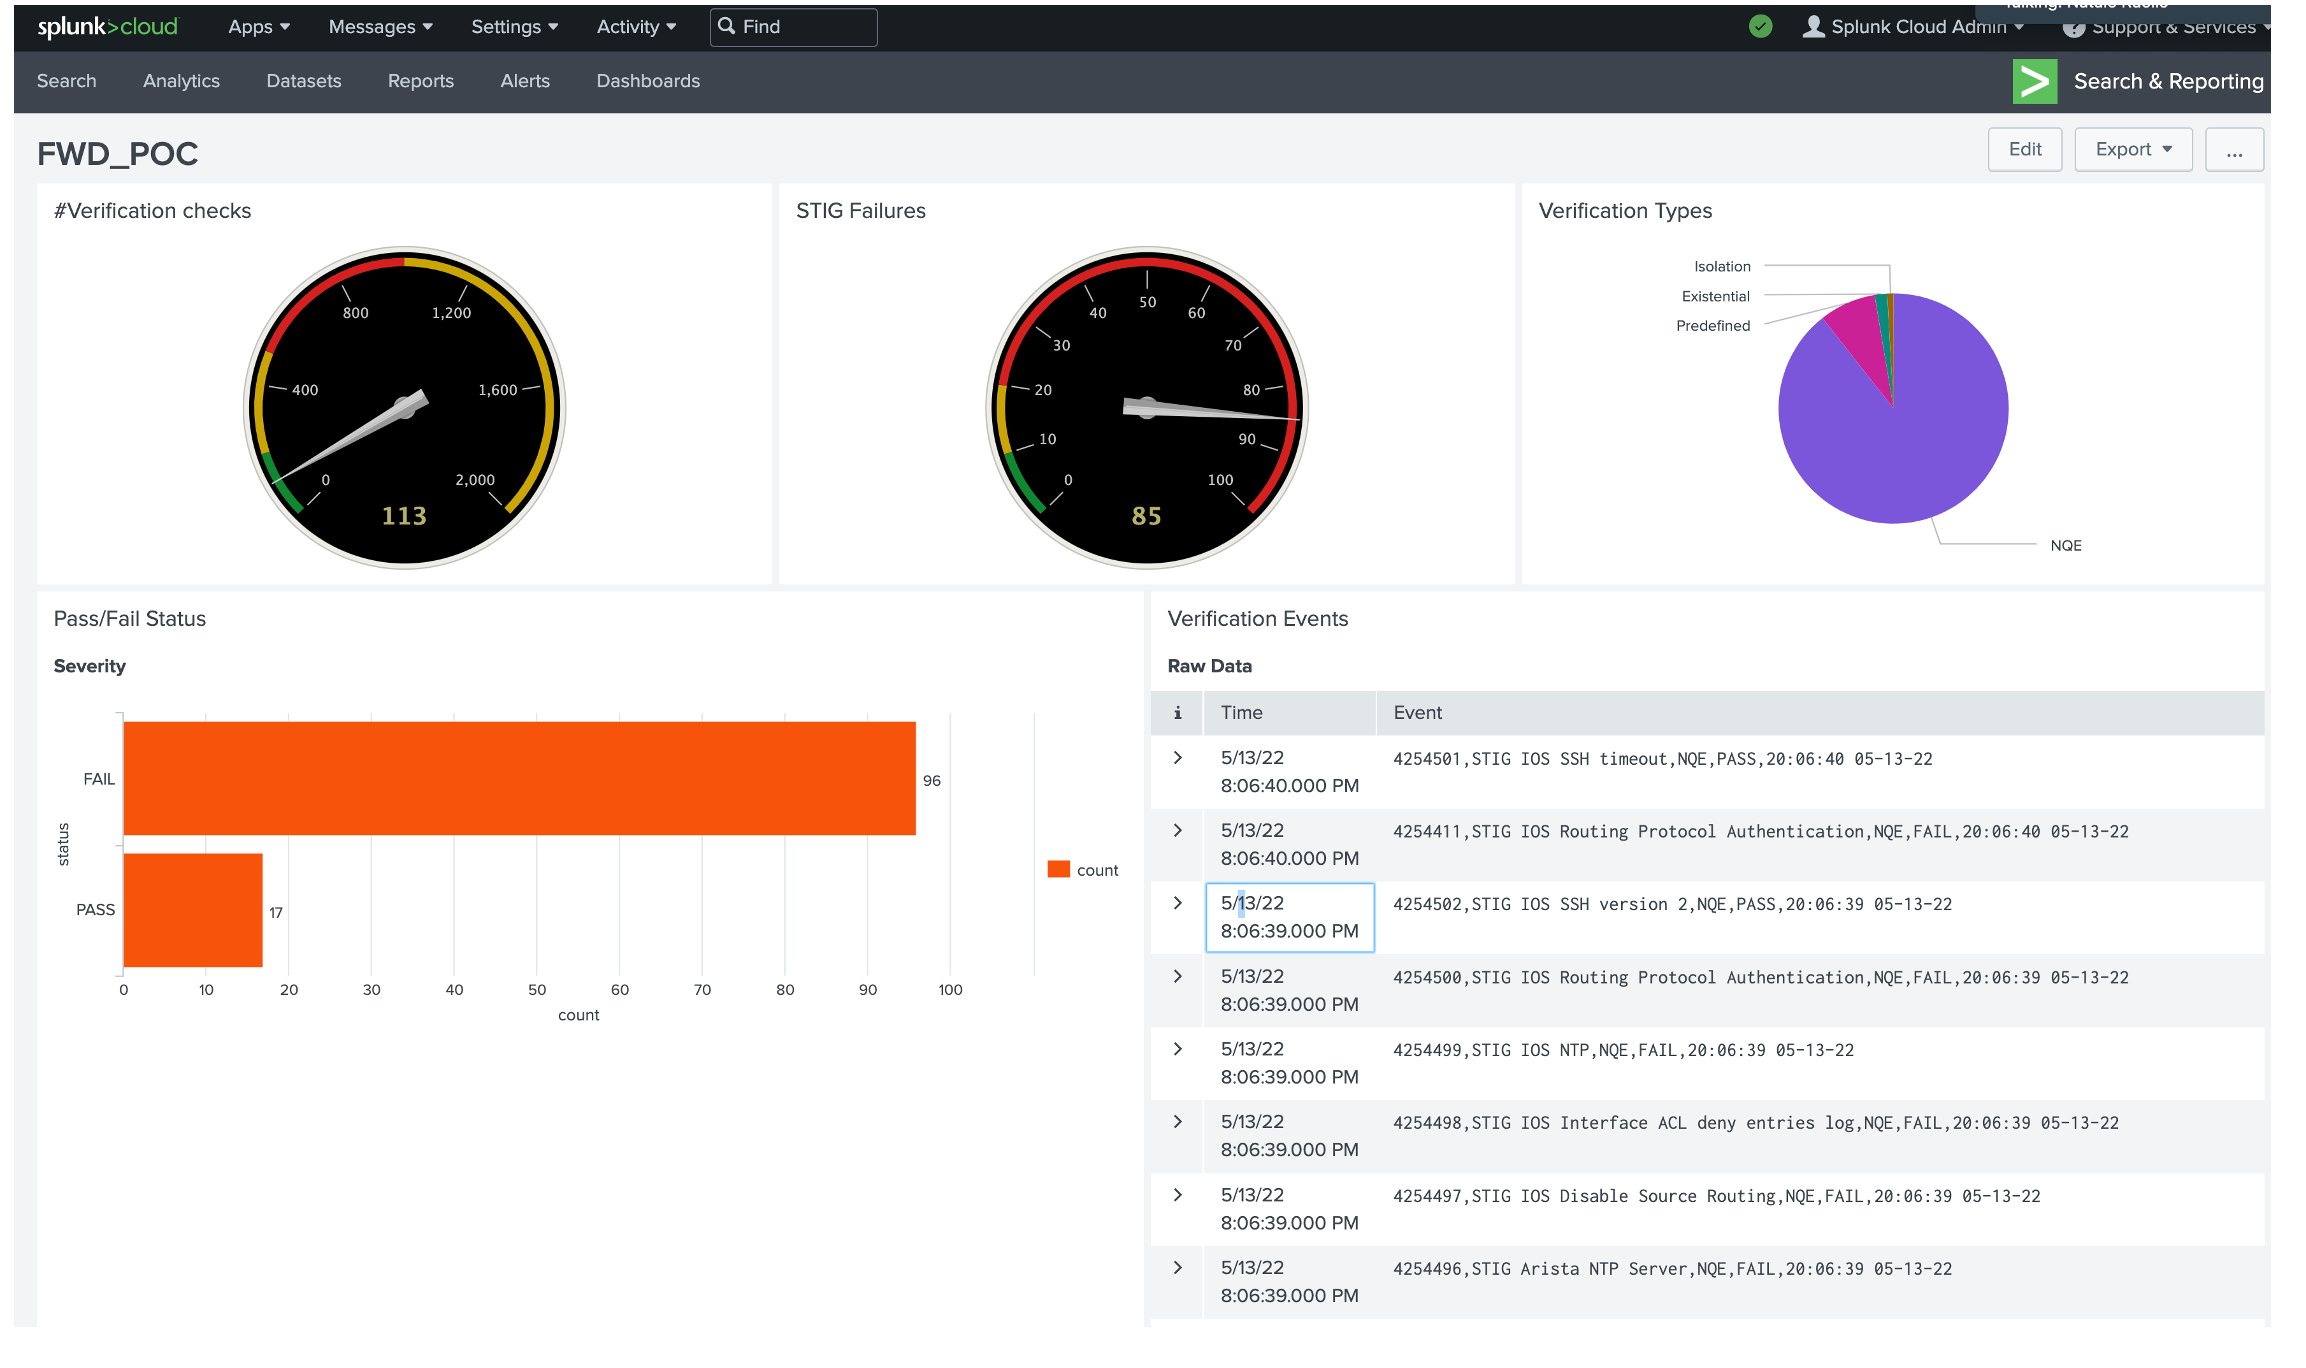
Hi Kristopher. We have many customers that have successfully integrated with Splunk. At a very highlevel, an NQE query is developed to extract the desired data from the Forward Platform. The data is extracted in a structured format and easily ingested into Splunk via a 3rd party Splunk app accessing the data through Splunk forwarders. Before developing the 3rd party app, I suggest creating the query an ingesting through the Splunk Web interface to ensure the proper visualization, indexing, etc. is achieved.
In this example, The customer wants to ensure that best practices for device hardening are followed. We begin by ingesting the NQE output compliant with the best practices and from this point simple dashboards are created for simple at-a-glance consumption.
Badge winners
Sign up
Already have an account? Login
Welcome to the Forward Networks Community
Select a login option:
Register / Login Forward Employee LoginEnter your E-mail address. We'll send you an e-mail with instructions to reset your password.